
What Does a Data Breach Really Cost in 2026?
We will discuss the core key points of Cost of a Data Breach Report by IBM; we will understand and see what the cost of a data breach is and where the money goes. How time matters, how AI is being used, etc.
Most people don’t understand how serious a data breach is. They have different opinions, and most of them don’t know how this happens.
To understand how a data breach occurs, we have covered so many topics on understanding cybersecurity basics; you can learn from them.
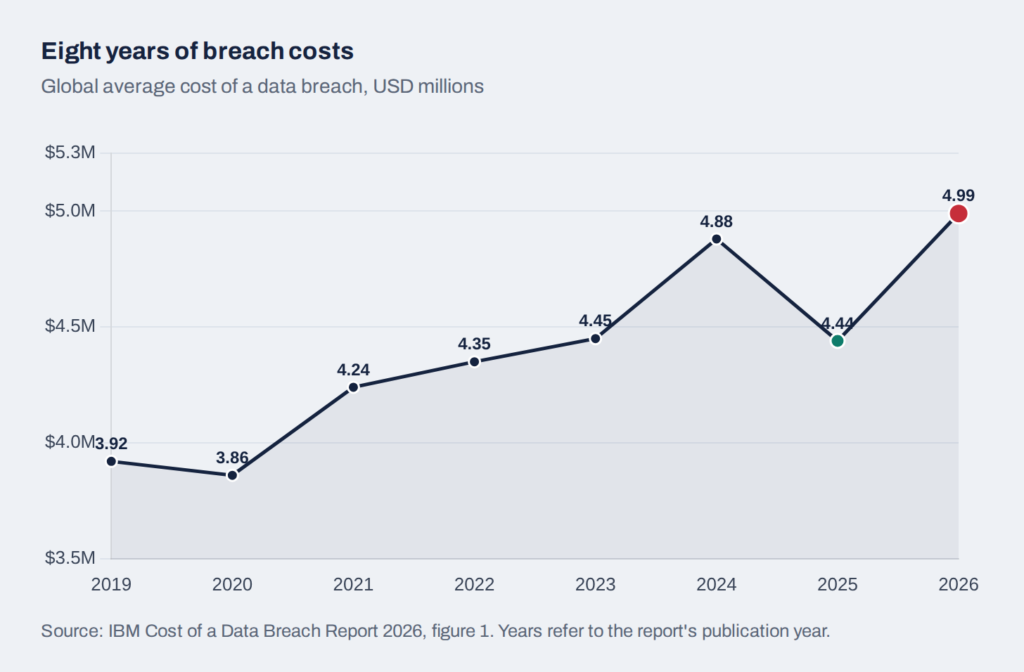
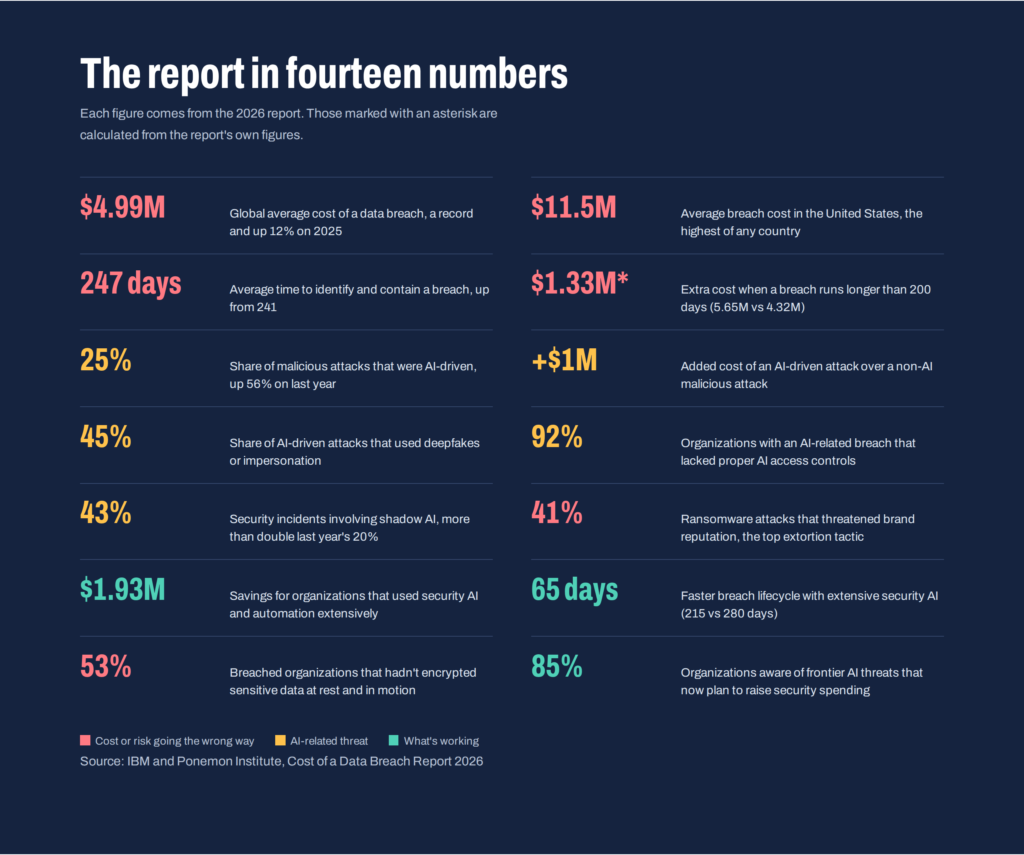
According to IBM’s 2026 report, the average cost of a data breach is $4.99 million. This is the highest in the 21 years the report has been running.
What is the Cost of a Data Breach Report?
Every year, IBM and the Ponemon Institute conduct studies and research about the companies that have been breached.
A data breach is when a company’s data, such as employee names or customer details, is stolen or exposed. Most breaches are caused by attackers, but some come from human error or IT failures.
This year, they studied 602 organizations in 16 countries and 17 industries, for breaches that happened between March 2025 and February 2026.
They didn’t send out a survey. Instead, they interviewed people who dealt with those breaches directly, such as security teams, finance heads, and other leaders involved in the breach.
So these numbers come from the people who were involved directly and cleaned up the breach.
Where does USD 4.99 million go?
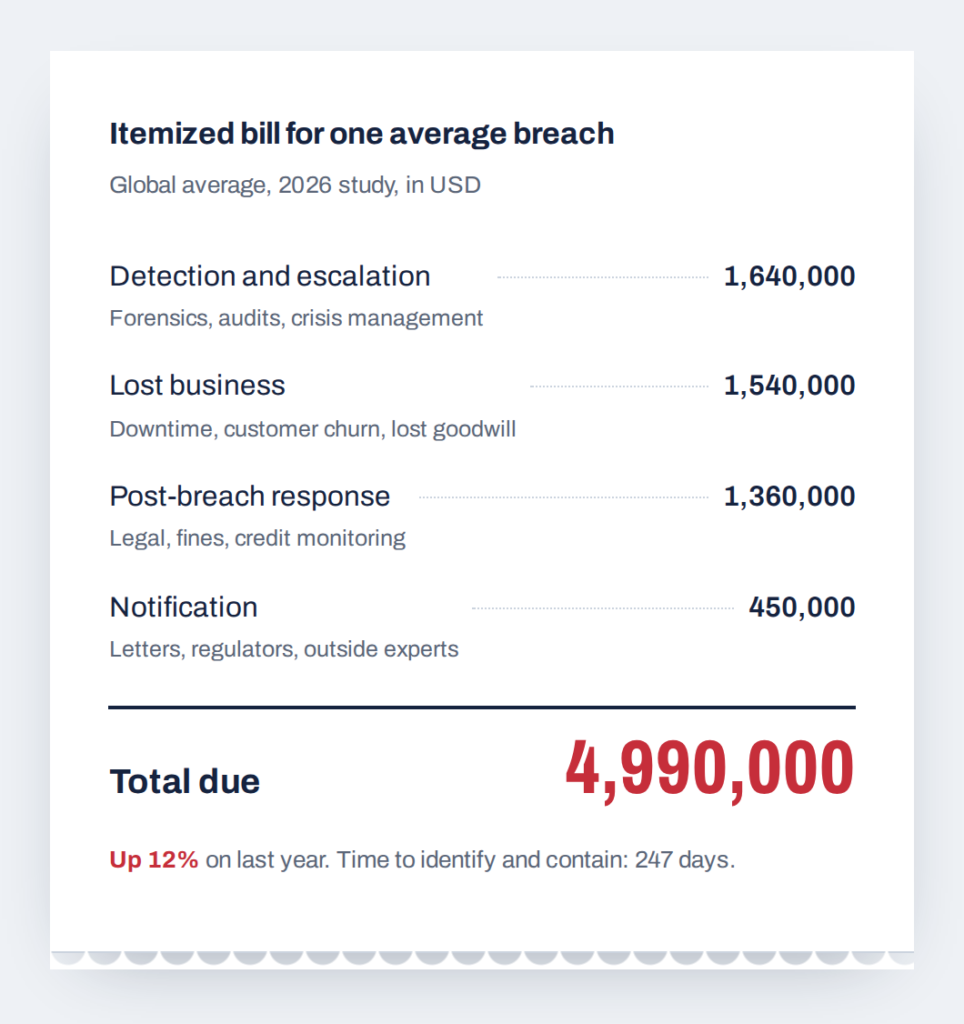
The $4.99 million does not go to the hackers. It is the total cost to the company because of the breach.
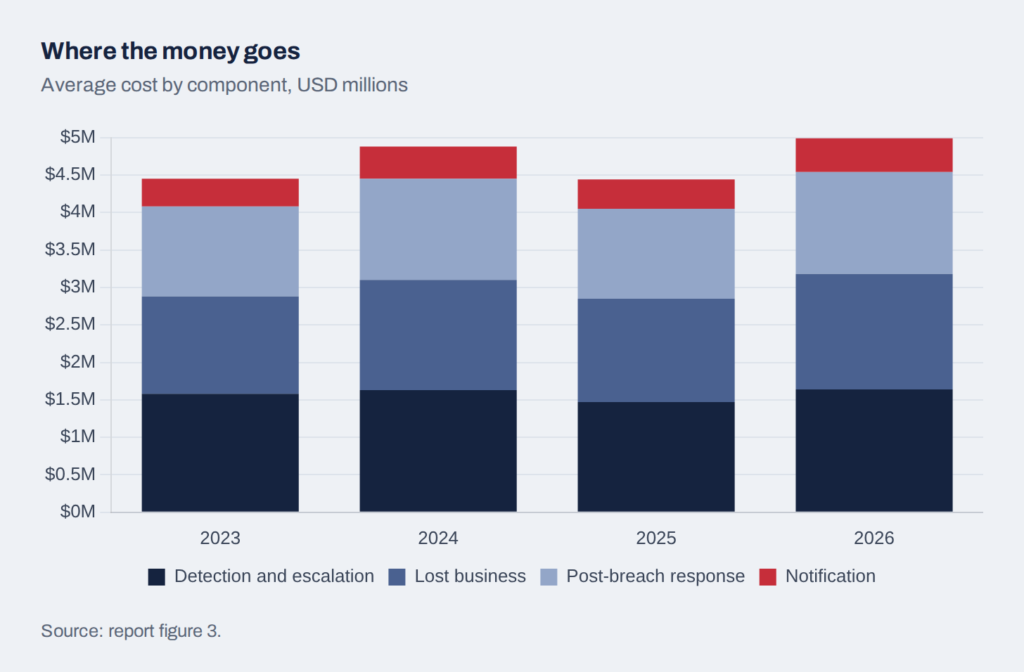
The report splits the cost into four parts. Detection and lost business together make up about 63% of the total:
- Detection and escalation: USD 1.64 million. When a breach occurs, the company has to find out what happened. So it pays for forensic experts, audits, and meetings with the board.
- Lost business: USD 1.54 million. Systems go down. Customers leave. People stop trusting the brand.
- Post-breach response: USD 1.36 million. After the data breach, a company pays for lawyers, regulatory fines, and credit monitoring for affected customers.
- Notification: USD 0.45 million. This is where a company tells people their data was exposed, by letters, emails, and calls.
All these costs went up this year. The total rose 12% compared to last year.
Last year, costs dropped for the first time in five years, to USD 4.44 million. Many people took that as a sign that defenders were winning, but this year shows it was just a pause.
Does it cost the same everywhere?
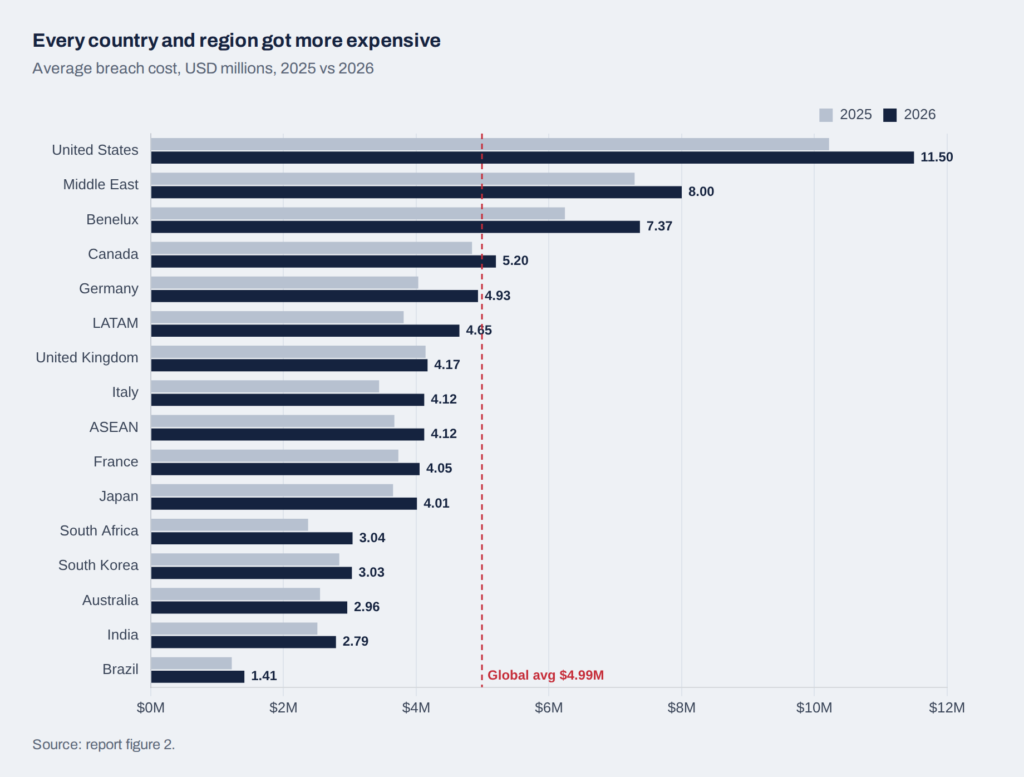
The United States has the highest cost, at $11.5 million per breach. This is more than double the global average. Higher regulatory fines and higher business costs are the main reasons.
The Middle East (USD 8 million) and Benelux (USD 7.37 million, up from USD 6.24 million) are next. Benelux includes Belgium, the Netherlands, and Luxembourg.
Costs rose in every country and region in the study.
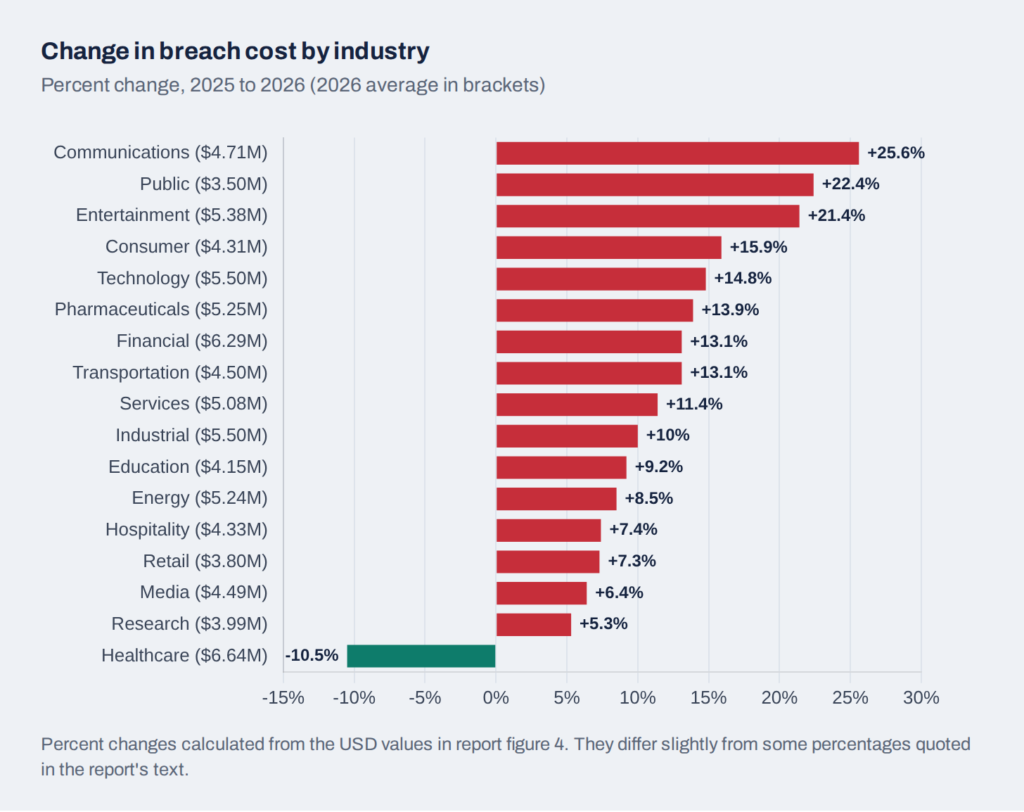
Healthcare is the most expensive industry for the 13th year in a row, at USD 6.64 million per breach. Note that this is down from USD 7.42 million last year. It was the only industry where costs fell.
Patient data are valuable to criminals because they can be used for identity theft and insurance fraud.
Financial services came next at $6.29 million, up from $5.56 million.
Why does time matter so much?
We have already discussed how time matters in an attack.
The longer a breach lasts, the more it costs.
Here we can split time into two stages.
If you want to see the full attack from the attacker’s side, read our post on how cyberattacks work.
Stage 1 — Identify: finding the breach
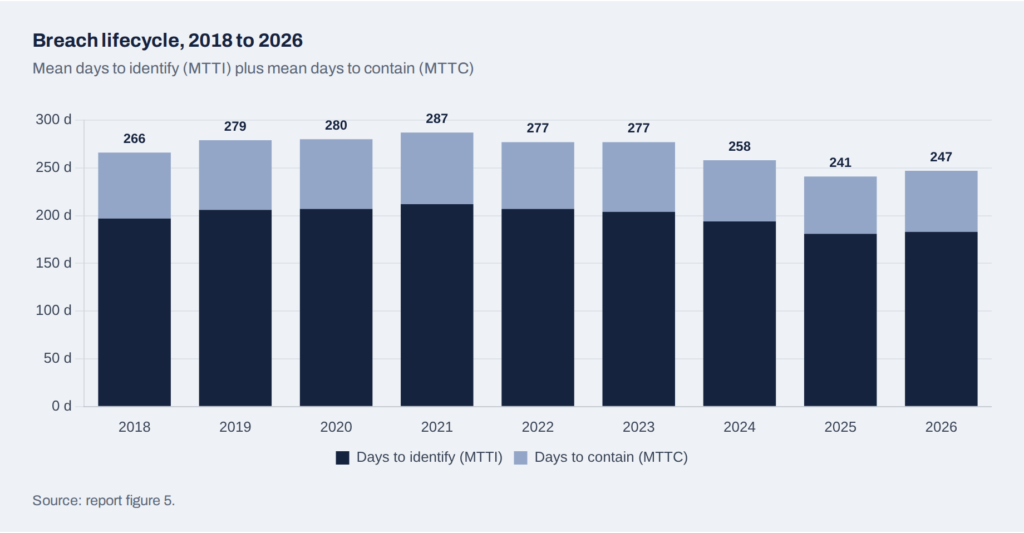
It took 183 days on average for companies to find that there is a breach.
That is about six months where the attacker is inside, and nobody knows.
Stage 2 — Contain: stopping the damage
It takes another 64 days for the companies to shut down the breach completely.
That brings the total to 247 days, 6 days longer than last year. This is the first rise in five years.
Now compare that to the money spent. Breaches contained in under 200 days cost USD 4.32 million. Breaches that took more than 200 days cost USD 5.65 million.
That’s an extra USD 1.33 million for being slow.
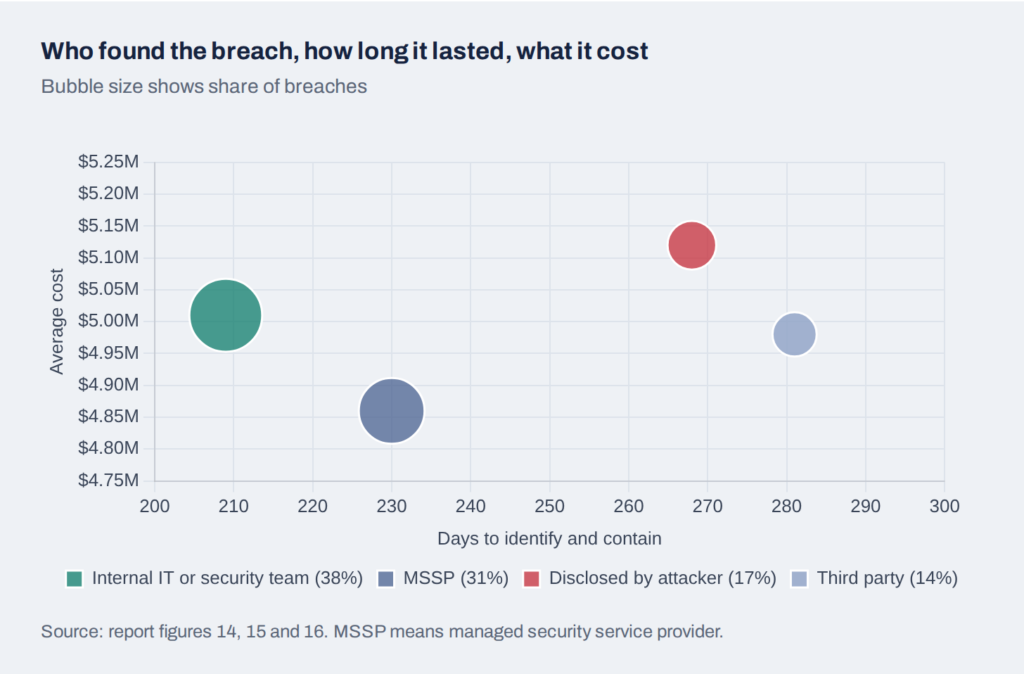
If a company’s own security team finds the breach, the whole process takes 209 days.
But in 17% of cases, the company only finds out when the attacker tells them, for example with a ransom note. These breaches take 268 days to identify and contain.
They also cost more, at USD 5.12 million on average.
Quick summary. Found by your own team = faster and cheaper. Found by the attacker = slower and more expensive.
How are attackers using AI?
The rise of AI in attacks is spiking.
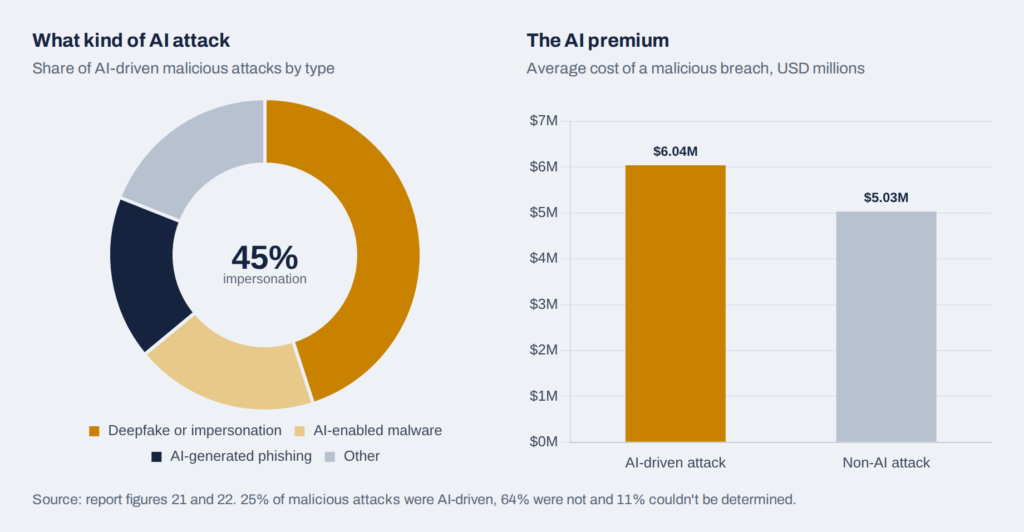
According to IBM, 1 in 4 malicious breaches involved AI. That is a 56% increase from last year.
Many people think attackers mainly use AI to write malware. That is not the case.
The main use is pretending to be someone else.
Deepfakes and impersonation: This accounts for 45% of AI-driven attacks. A deepfake is a video or voice made by AI that looks and sounds like a real person.
AI-enabled malware: 19%. Malware is harmful software; AI now helps to write, build, and run the malware.
AI-generated phishing: 17%. Phishing is an old trick of hacking, where the attacker sends an email with a fake link attached. Read on what phishing is here. Now, AI writes phishing emails and messages.
Can your own AI tools be attacked?
Yes, and this segment has seen a rise.
21% of organizations reported that there was a breach that involved their own AI models. Last year it was 13%.
Model inversion: USD 6.07 million on average. In this, the attacker asks clever questions until the AI reveals its private data.
Prompt injection: USD 5.89 million. The attacker hides instructions in text the AI reads, like an email or a web page. The AI then follows the attacker instead of its owner.
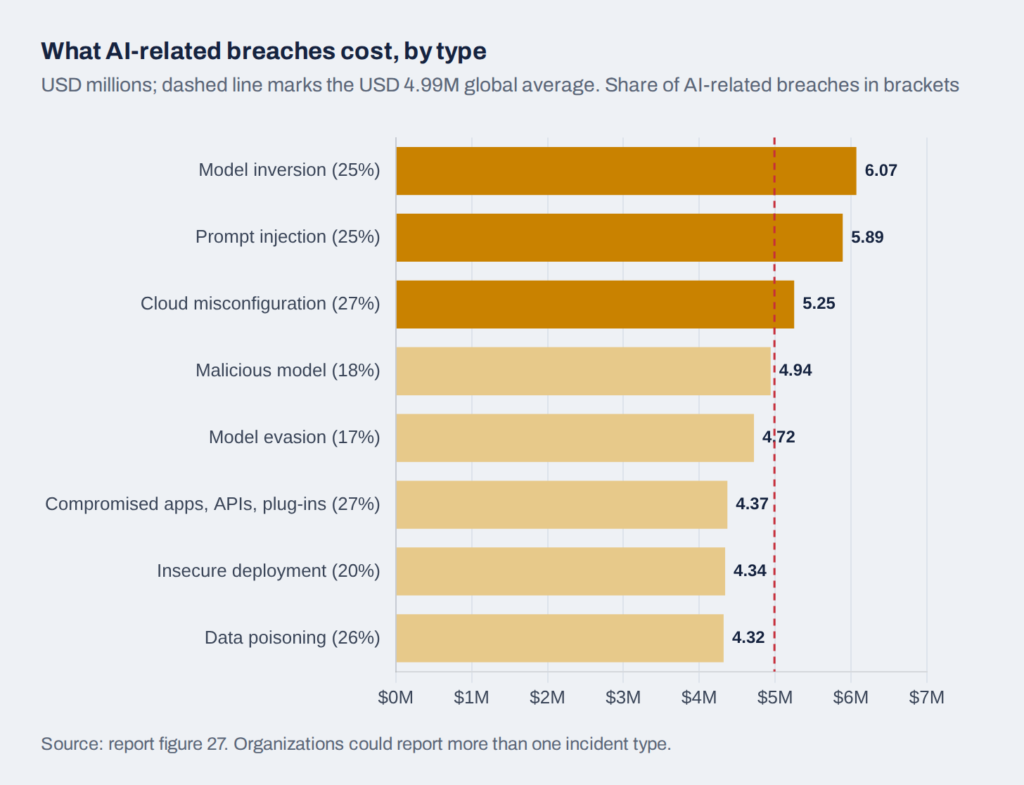
Note that the most common causes were not fancy AI tricks.
They were basic mistakes. Compromised connections between apps, known as APIs, and wrong cloud settings each caused 27% of these breaches.
The report found that 92% of organizations with an AI-related breach did not have proper access controls on their AI. Access control simply means deciding who is allowed to use what.
In other words, many companies left the door unlocked.
Then there is shadow AI. This is when employees use AI tools the company never approved. Think of someone pasting customer data into a personal chatbot account to save time.
Incidents involving shadow AI more than doubled, from 20% to 43%.
Is AI helping defenders too?
Yes, and this is the good news.
Companies that used security AI and automation extensively had breaches that cost USD 4 million on average. Companies that used none paid USD 5.93 million. Note that only about a third of companies use these tools extensively.
That is a saving of USD 1.93 million. They also dealt with breaches 65 days faster.
But there is a problem.
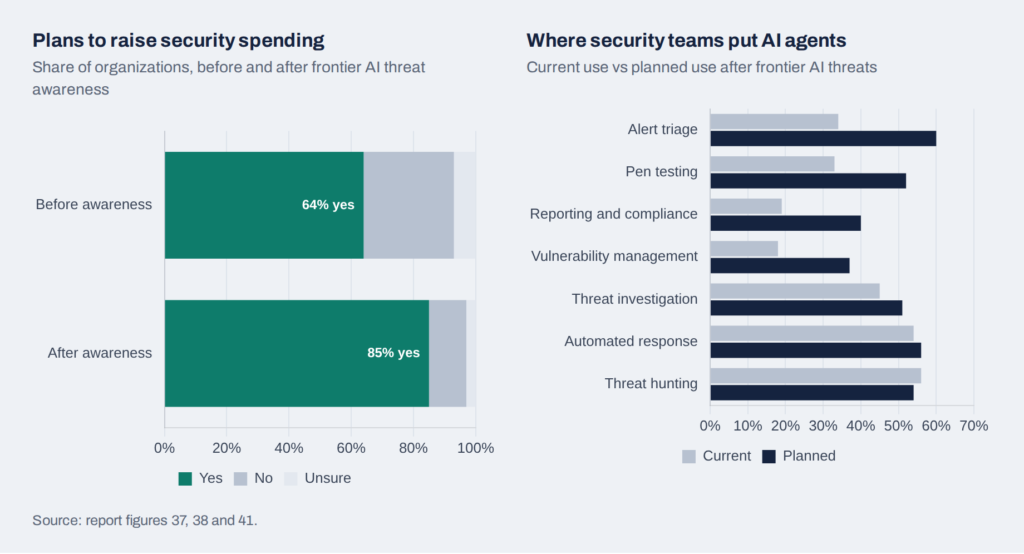
Most companies use AI in the wrong place. They use it to detect and investigate attacks after they start. Very few use it to prevent attacks in the first place.
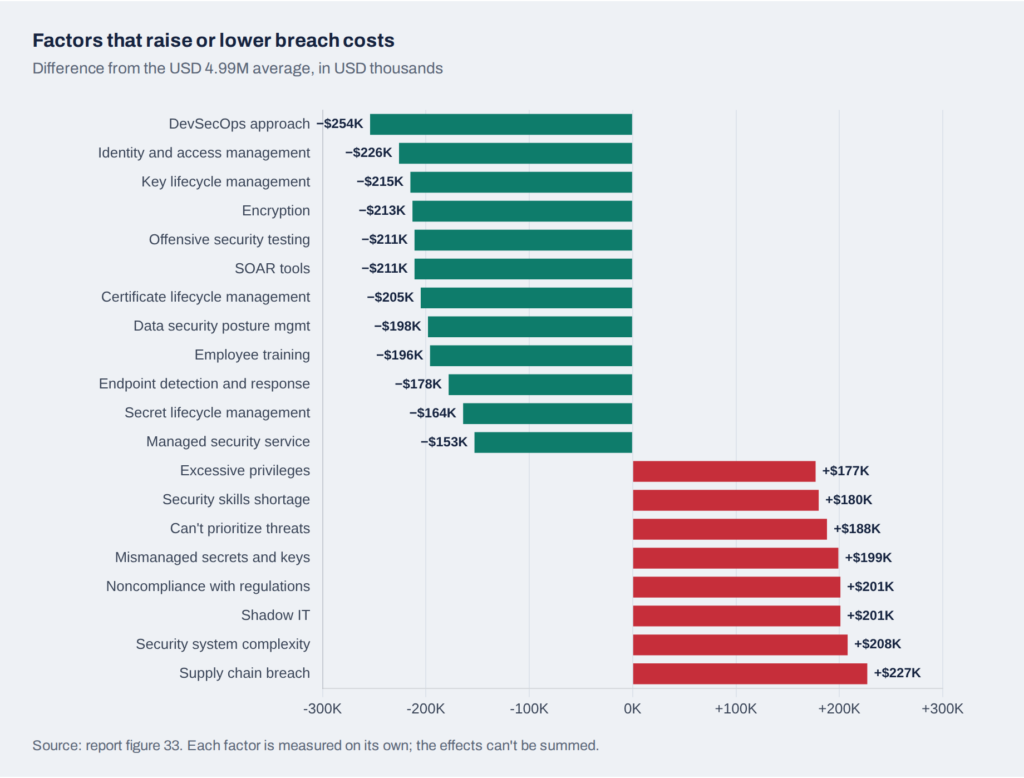
Half of companies now use AI agents in their security operations. An AI agent is an AI that can take actions on its own, not just answer questions. But only 18% of them use agents to find and fix weaknesses in their systems.
That is exactly the job attackers are now giving to AI.
In April 2026, Anthropic announced Claude Mythos Preview, a frontier AI model that had already found thousands of high-severity security holes. Some were in every major operating system and web browser. A frontier model simply means one of the most advanced AI models available.
If you want to know why unknown security holes are so dangerous, read our post on what a zero-day is.
If attackers can find weaknesses at machine speed, defenders need to fix them at machine speed. We will discuss AI agents in security in later posts.
You might be thinking: “I’m not a big company. Why should I care?”
Fair question.
Most of these attacks start with a person. A phone call. A text message. A fake video of your boss.
In the report, phishing, including voice and SMS phishing, was the most common way attackers got in. Voice and SMS phishing also led to the most expensive breaches, at USD 5.29 million on average.
Those same tricks work on you at home. The attacker does not care how big you are. They care whether you will click, pay, or share.
A real case: the deepfake video call
In January 2024, an employee in the Hong Kong office of the engineering firm Arup received a message. It appeared to come from the company’s chief financial officer in the UK. It asked for a confidential transaction.
The employee was suspicious. That was the right instinct.
So a video call was arranged. On the call were the CFO and several colleagues the employee recognized. They looked real. They sounded real.
Reassured, the employee made 15 transfers to five bank accounts. The total was about HK$200 million, roughly USD 25 million.
Every other person on that call was a deepfake.
The scam was only discovered when the employee later checked with head office. By then, the money was gone.
This is the 45% from the report, in real life. And the fix is almost free. Before moving money, call the person back on a number you already know.
Can we trust these numbers?
Mostly yes.
The study is a benchmark, not a scientific survey. The costs are estimates from the people interviewed, not audited accounts. It also leaves out very large breaches with more than 115,380 records.
Some groups are small, too. For example, the Benelux figures come from only 34 organizations.
A few percentages in the report’s text also don’t match its own tables. For example, the US cost rose from USD 10.22 million to 11.50 million. That is 12.5%, but the text says 11% in one place and 13% in another.
The overall trends are clear. Just check the exact number before you quote it.
What can organizations do?
The report points to four steps:
- Use AI to prevent attacks: Start with finding and fixing weaknesses, not just spotting attacks.
- Protect every identity: This includes non-human identities. These are accounts used by software, like service accounts and API keys. Less than half of companies (46%) secure them in their AI systems.
- Control your AI: Know which AI tools are in use, approved or not. Lock down the settings and connections around them.
- Fix encryption now: Encryption scrambles data so only the right people can read it. 53% of breached companies had not encrypted their sensitive data both at rest and in transit. Only 26% have started a project to prepare for quantum computers, which may one day break today’s encryption.
Final thoughts
The average breach now costs USD 4.99 million. But the bigger lesson of this report is speed.
Attackers now move at machine speed. Every day a breach goes unnoticed adds to the bill.
For companies, that means using AI to find weaknesses before attackers do. For you, it means slowing down. If a call, a message or even a video asks you to move money or share details, stop and check.
References
- IBM and Ponemon Institute, Cost of a Data Breach Report 2026: The AI tipping point. https://www.ibm.com/reports/data-breach
- CNN, “Finance worker pays out $25 million after video call with deepfake ‘chief financial officer’,” 2024.
- South China Morning Post, report on the Hong Kong deepfake video meeting scam, February 2024. https://www.scmp.com/news/hong-kong/law-and-crime/article/3250851/everyone-looked-real-multinational-firms-hong-kong-office-loses-hk200-million-after-scammers-stage
- IBM Newsroom: One in four malicious breaches are AI-enabled (July 2026)
- Simon Willison: Anthropic’s Project Glasswing and Claude Mythos Preview (April 2026)